Independent neobanks trail traditional banks by 28.1 percentage points on serious app security findings, despite leading on passkeys and attestation.…
Blog
Ostorlab Blog
Vulnerability research, CVE deep dives and engineering write-ups from the Ostorlab team on AI pentesting and mobile, web and API security testing.
Ostorlab Research
Ostorlab Blog
Vulnerability research, CVE deep dives and engineering write-ups from the Ostorlab team on AI pentesting and mobile, web and API security testing.
- Articles
- 380
- CVE deep dives
- 141
- Critical CVEs analysed
- 81
- Publishing since
- 2015
Featured
Featured Stories
How Apple FairPlay encrypts iOS app binaries, what is documented, and why one reusable account credential unwraps every app it owns.
ARTEX went from a July GitHub release to bank breaches, a ConnectWise supply-chain compromise and a 200-targe…
An A2B (App-to-Backend) attack analyses a public mobile app, extracts its API endpoints and embedded keys, th…
A mobile app can run in a hostile environment even when its binary is intact. Ostorlab’s open-source RASP let…
Start here
Collections
Years of research, grouped by subject. The most read first.
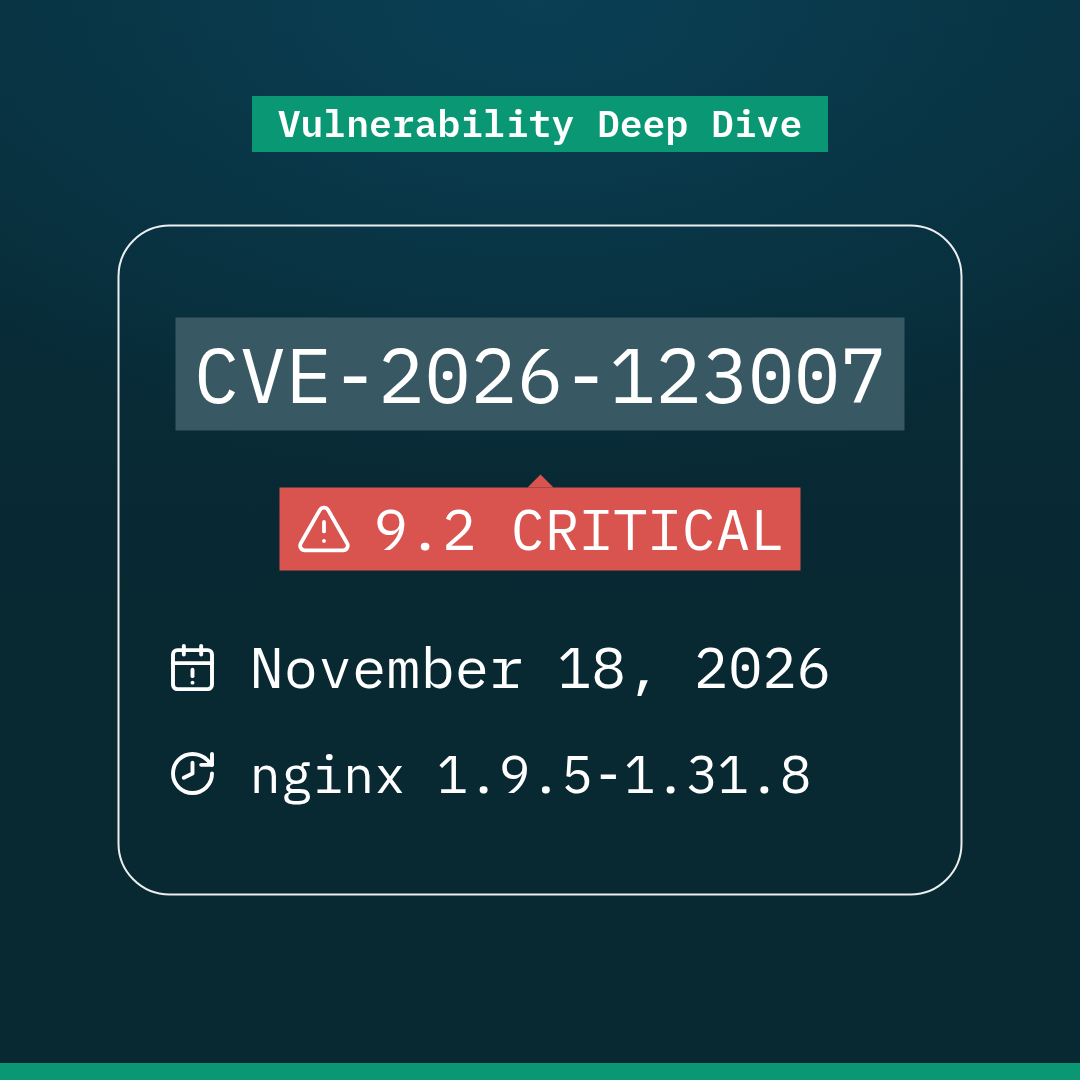
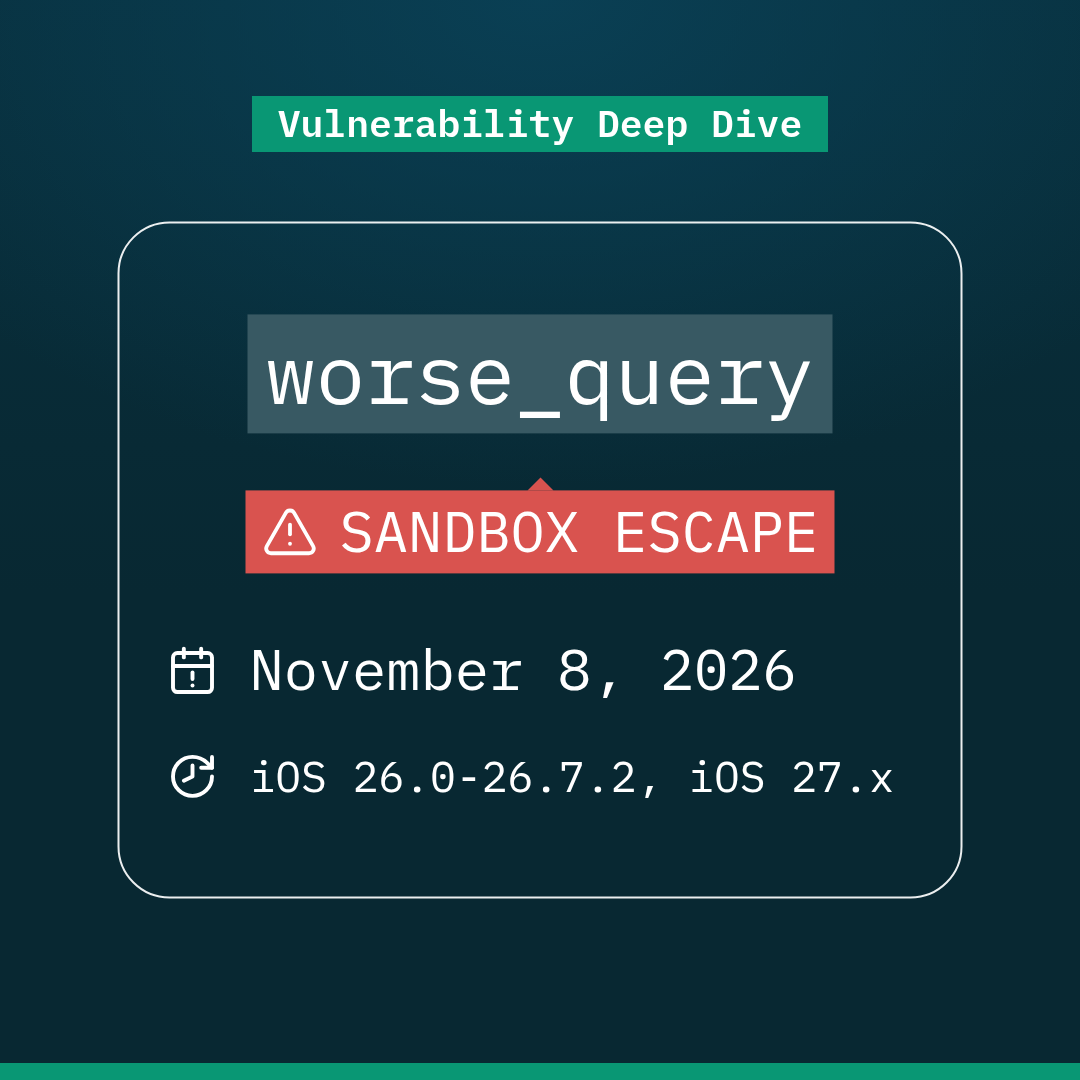
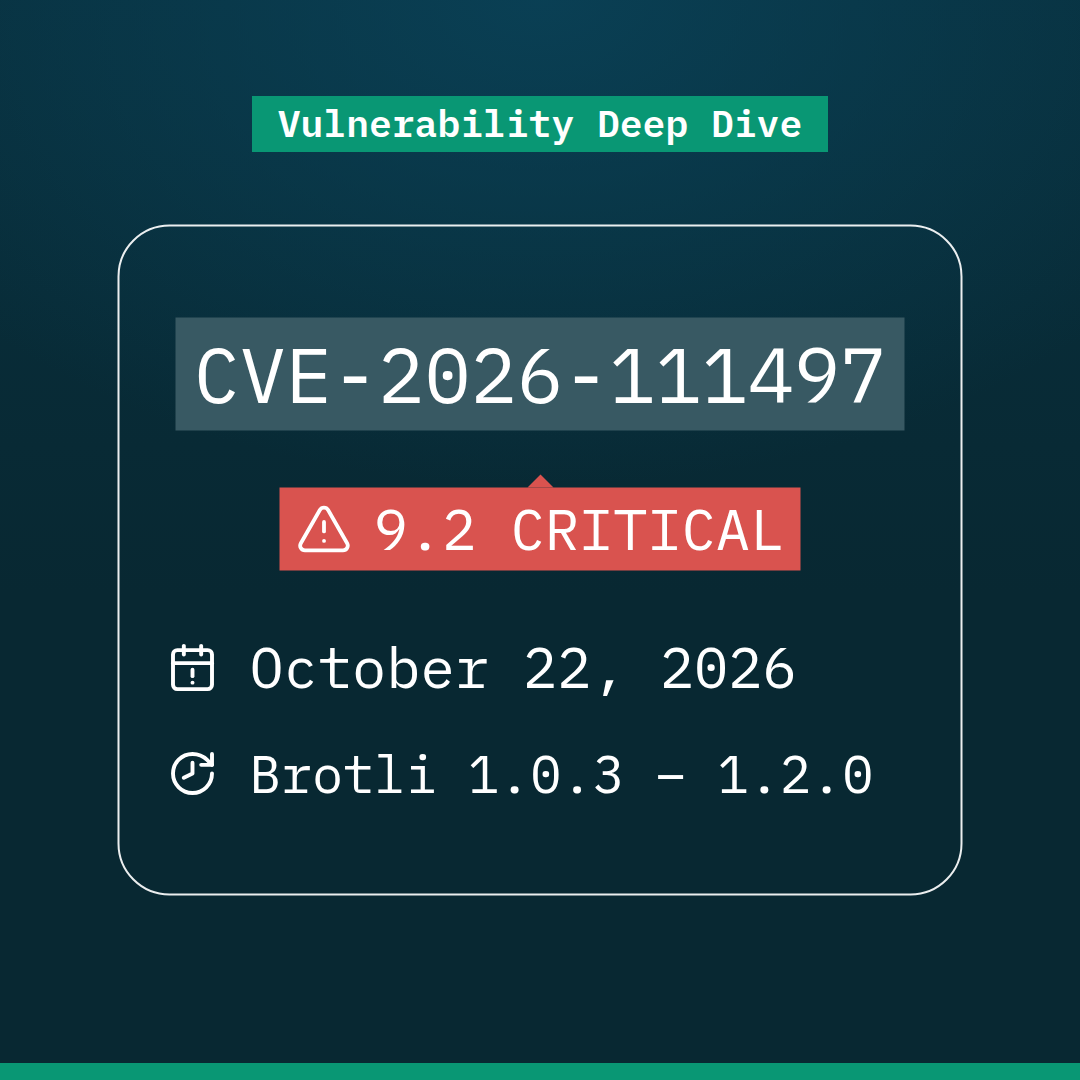
Who is affected, how to fix it and how the flaw works.
How AI agents find, exploit and prove vulnerabilities.
Mobile internals, attacks and how to test apps.
Injection, access control and API attacks, explained.
Industry studies and open benchmarks, with the data.
The library
Explore all research
Showing 12 of 380
 Deep Dive
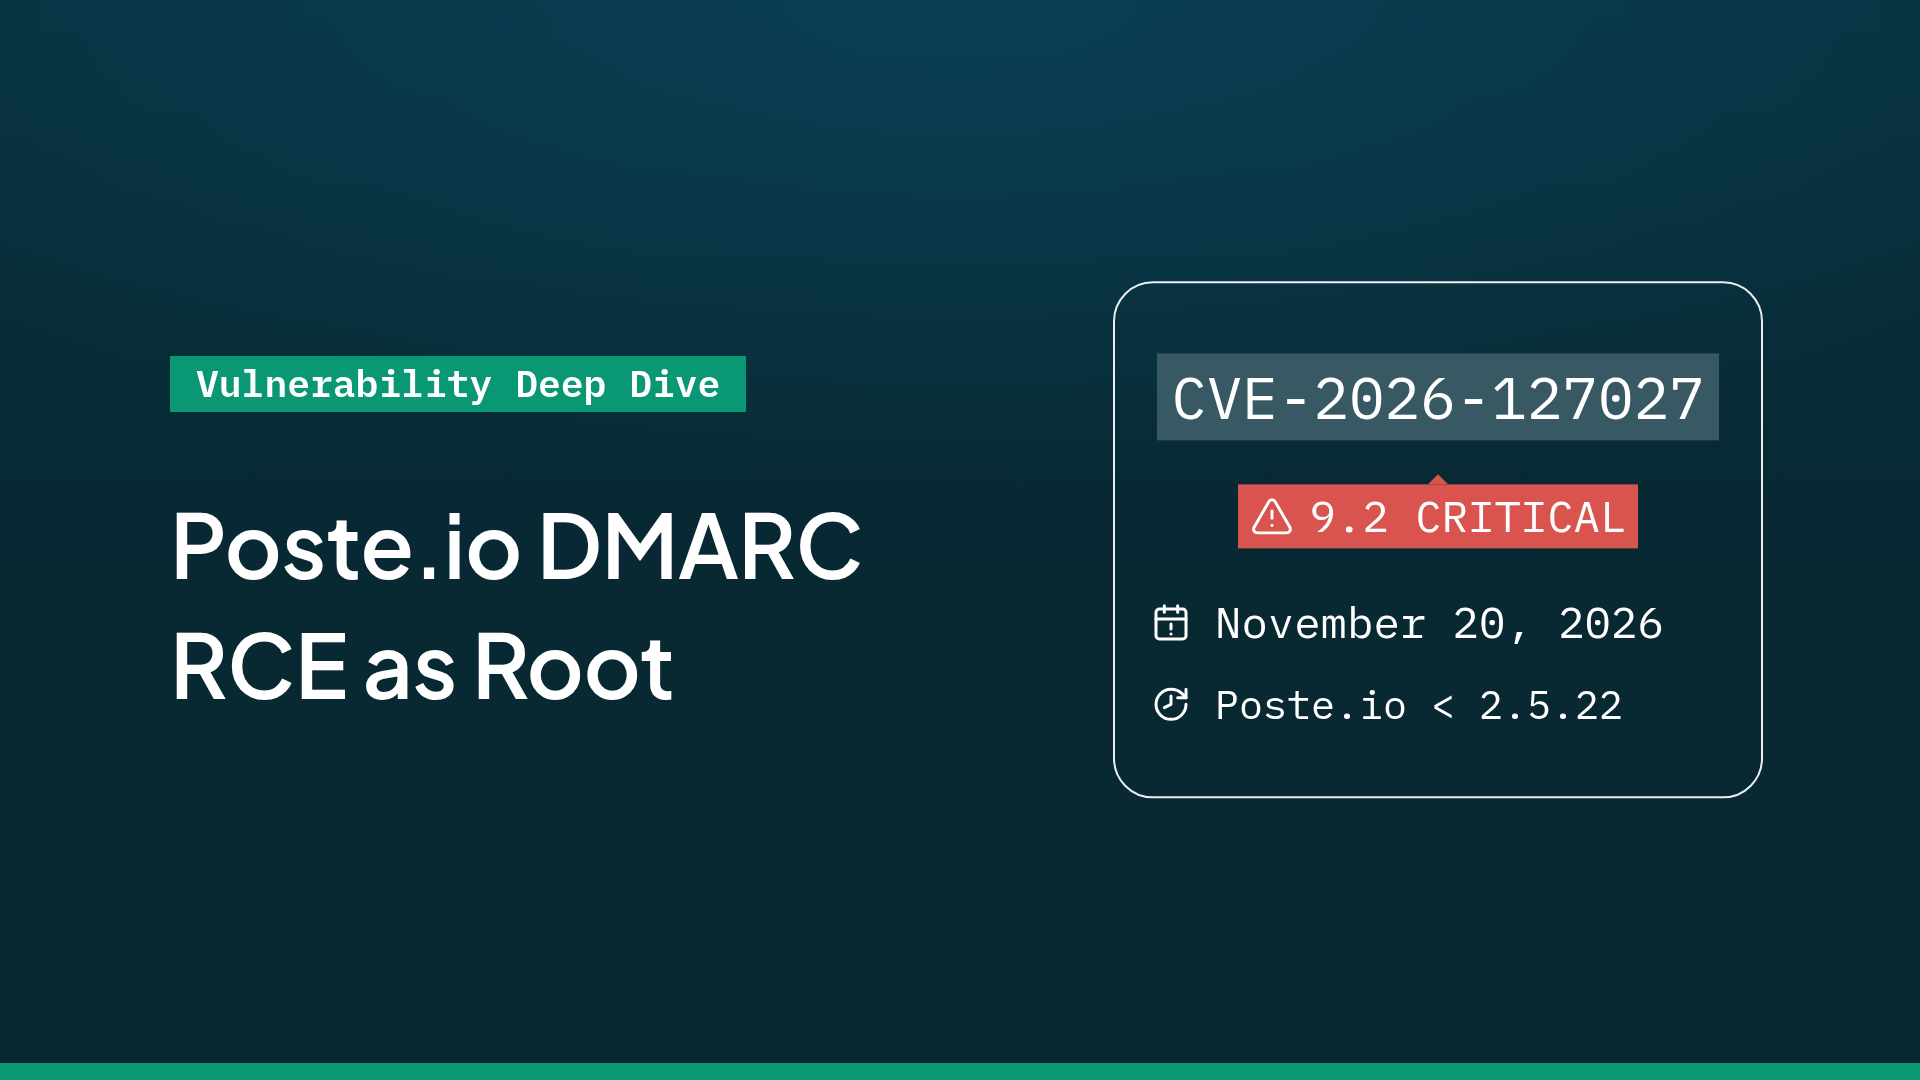
Poste.io DMARC RCE as Root, Fixed in 2.5.22 (CVE-2026-127027)
Poste.io before 2.5.22 runs a root shell script on DMARC report attachments, so an unauthenticated email can inject com…
Nov 20, 2026
 Deep Dive
Pocket ID Email Verification Bypass, Fixed 2.12.0 (CVE-2026-115770)
Pocket ID before 2.12.0 keeps an email-verification token valid after the address changes, letting a user verify an add…
Nov 20, 2026
 Deep Dive
Apache Axis 1.x SOAP Fault RCE, Exploited (CVE-2026-90436)
Apache Axis 1.x loads and instantiates the class named in an unauthenticated SOAP fault, enabling RCE; migrate or apply…
Nov 20, 2026
 Deep Dive
Cisco Expressway Root RCE Exploited in the Wild (CVE-2026-76466)
An unauthenticated attacker can join a clustered Cisco Expressway database and run commands as root; exploited in the w…
Nov 20, 2026
 Deep Dive
Refitter OpenAPI Code Injection RCE (CVE-2026-63344)
A crafted OpenAPI description makes Refitter emit a C# module initializer, so the generated client runs attacker code a…
Nov 20, 2026
 Deep Dive
Chrome Sandbox Escape: Android WebView Impact (CVE-2026-9998)
Chrome 148 fixes two sandbox escapes, including a Skia SkSL flaw that ships in Android WebView; fixed in 148.0.7778.215…
Nov 20, 2026
 Deep Dive
NLTK JAR Sandbox Bypass, Fixed in 3.10.4 (CVE-2026-128138)
NLTK 3.10.3's java() helper trusts the first cmd token, so a crafted -jar or @argfile runs an external JAR; fixed in 3.10.4.
Nov 20, 2026
 Deep Dive
VMware vCenter Auth Bypass Exploited in the Wild (CVE-2026-123890)
An unauthenticated vCenter Directory Service flaw yields administrator@vsphere.local; exploited as a zero-day, fixed in…
Nov 20, 2026
 Deep Dive
Drupal Core Installer Reinstall RCE (CVE-2026-132165)
Drupal's installer can treat an unverifiable database as a fresh site and let an unauthenticated visitor reinstall it; …
Nov 20, 2026
 Deep Dive
phpAfterShell: PHP Session File RCE (CVE-2026-126714)
An interrupted PHP session write can splice two sessions into one file, letting an attacker inject objects at session_s…
Nov 20, 2026
 Deep Dive
Etherpad Pre-Auth File Read to RCE (CVE-2026-114516)
Etherpad before 3.3.3 lets an unauthenticated attacker read any file through /static and escalate to admin code executi…
Nov 20, 2026
 Deep Dive
PHP-FPM Request Smuggling RCE, Fixed in 8.5.13 (CVE-2026-129289)
Unread request bodies let an attacker smuggle a FastCGI request past the front end and run PHP as the worker; fixed in …
Nov 19, 2026
Newsletter
The Breach Brief
Offensive AI and cybersecurity breakdowns curated by Ostorlab every two weeks.
Partner Man: The €100M Heist
Nov 18, 2026
Who Changed the Recipe?
Nov 04, 2026
Japan: Cyber Crisis Boils Over
Oct 21, 2026
Data, on the House
Oct 07, 2026Product
Changelog
Early November 2026: Open-Source RASP, the 2026 Banking Report and New CVEs
What shipped
- Our RASP is now open source
- The 2026 Mobile Banking App Security Report
- We now find and disclose vulnerabilities in open-source software
- SMS codes reach your scans before they expire
- A new overview for every scan
- Risk lineage: see what a risk is built from
- + 4 more
- Oct 31, 2026 · 11 changes · Video Late October 2026: Cloud Inventory, Scheduled Testing and Investigation Replay Free scanning for websites, source code and mobile app vetting · A clearer scan setup, from target to Start
- Oct 17, 2026 · 8 changes · Video October 2026: From Security Findings to Tested Fixes We added approvals to control dangerous actions · We introduced Ticket Agent for autonomous automation
- Sep 02, 2026 · 11 changes New Dashboard UI, On-Premises Scanner, Agentic Scan Knowledge, Multi-Asset Scanning, Linear & MCP Integrations, and New Model Support New Dashboard UI: Cockpit, Focus Mode & Custom Dashboards · Keyboard Shortcuts & Fast Navigation
Featured Stories
See all articles →
79% vs 51%: Independent Neobanks Lag on App Security
Independent neobanks trail traditional banks by 28.1 percentage points on serious app security findings, despite leading on passkeys and attestation. Our study of 2,686 apps explains the gap.
Nov 12, 2026
How FairPlay Protects iOS App Binaries, and an Account-Level Weakness
How Apple FairPlay encrypts iOS app binaries, what is documented, and why one reusable account cr...
Nov 12, 2026
ARTEX: How a Free AI Pentest Framework Became an Attacker Staple
ARTEX went from a July GitHub release to bank breaches, a ConnectWise supply-chain compromise and...
Nov 13, 2026
Poste.io DMARC RCE as Root, Fixed in 2.5.22 (CVE-2026-127027)
Poste.io before 2.5.22 runs a root shell script on DMARC report attachments, so an unauthenticate...
Nov 20, 2026
Read by Topic
Latest from Engineering, Product & Security
Engineering
View all Engineering →
Inside Ostorlab’s Open-Source RASP for Mobile Apps
A mobile app can run in a hostile environment even when its binary is intact. Ostorlab’s open-source RASP l...
Nov 19, 2026
Building a Security Software Factory at Ostorlab
Ostorlab's security factory pairs detection engines with agent maintainers to reduce false positives, expan...
Nov 13, 2026
The True Cost of False Positives: Calculating the Engineering Tax of Noisy Scanners
False positives are an engineering-capacity problem, not only a scanner-quality problem. Learn how to measu...
Sep 28, 2026
Product
View all Product →
Introducing Mobile ADR: Protect a Mobile App Without Touching Its Code
Ostorlab is launching Mobile ADR, Mobile Application Detection & Response. Upload the APK, AAB or IPA you w...
Nov 16, 2026
Ostorlab vs. Manual Pentesting: More Critical Findings, Less Time, Lower Cost
Ostorlab reports more critical findings, shorter testing time, and assessment costs of one-tenth to one-for...
Oct 28, 2026
How to Vet a Third-Party Mobile App Before You Allow It in Your Company
A five-step mobile app vetting checklist for security teams (permissions, trackers, malware, data flows, st...
Oct 27, 2026
Security
View all Security →
A2B Attacks: How Attackers Reach Your Backend Through Your Mobile App
An A2B (App-to-Backend) attack analyses a public mobile app, extracts its API endpoints and embedded keys, ...
Nov 19, 2026
Mobile Banking App Security, 2025 vs 2026: What Changed
Banks fixed some of last year's most common app flaws, but biometric login got easier to bypass as it sprea...
Nov 18, 2026
n0n's Claims Against Visa, Mastercard and JPMorgan: What the Evidence Shows
n0n listed Visa, Mastercard and JPMorgan Chase with a 48-hour leak clock. Visa points to an APAC provider, ...
Nov 18, 2026
Changelog
View all changesOctober 2026: From Security Findings to Tested Fixes
Oct 17, 2026
The Breach Brief Newsletter
Offensive AI and cybersecurity breakdowns curated by Ostorlab every two weeks.
Partner Man: The €100M Heist
Nov 18, 2026
Who Changed the Recipe?
Nov 04, 2026
Japan: Cyber Crisis Boils Over
Oct 21, 2026
Data, on the House
Oct 07, 2026