Ostorlab's Security Scanner GitHub App,Ticket Aggregation V2, Copilot Launch, and Enhanced Security Features
February's update introduces Ticket Aggregation V2 and Ostorlab Copilot, alongside improvements to reporting capabilities and detection mechanisms. These updates enhance vulnerability management, user experience, and security analysis across the platform.

Ticket Aggregation v2 🎫
Released an enhanced version of our ticket aggregation system with improved flexibility:
- Introduced customizable ticket grouping configuration allowing users to define their aggregation logic.
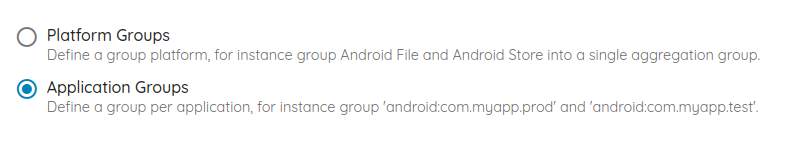
- Added granular false positive management with the ability to mark individual issues as false positives
Ostorlab's Security Scanner GitHub App 🛡️
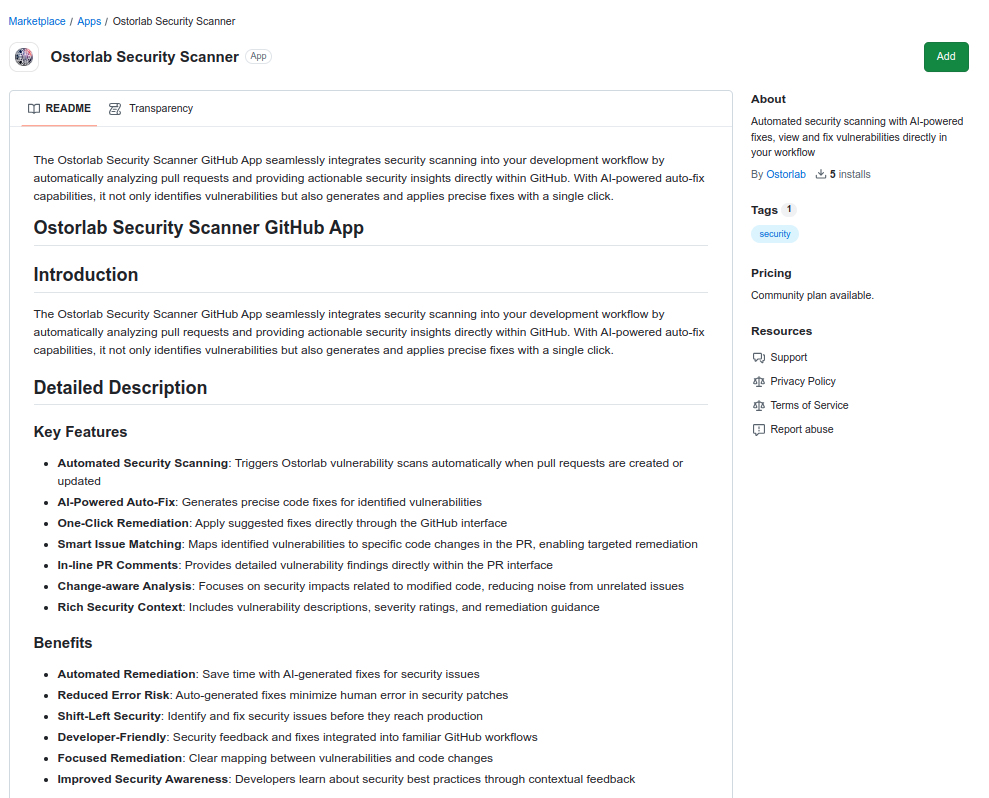
Released GitHub Security Scanner App for automated mobile app security scanning in CI/CD workflows:
- Automatic security scans triggered on pull requests and code pushes
- Direct vulnerability mapping to affected source code in PRs
- AI-powered explanation of security issues with fix suggestions
- Summary reports providing security posture insights
Copilot 🤖
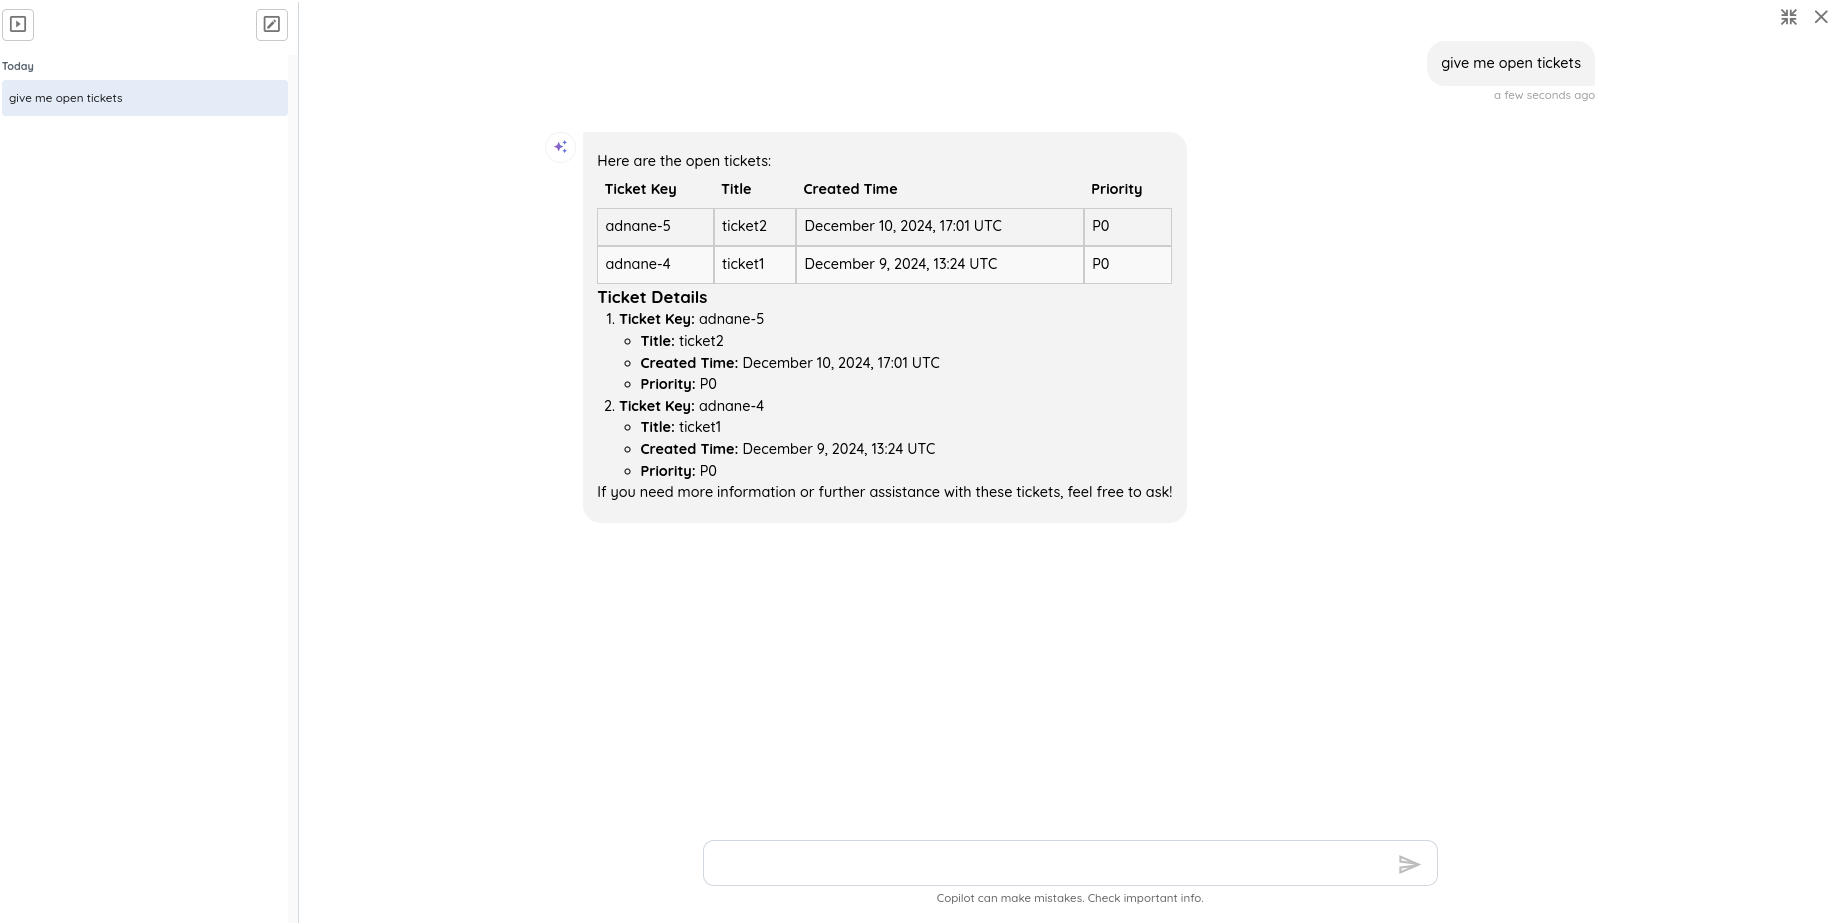
Launched our AI-powered assistant designed to enhance user experience:
- Provides documentation-based query responses for instant guidance
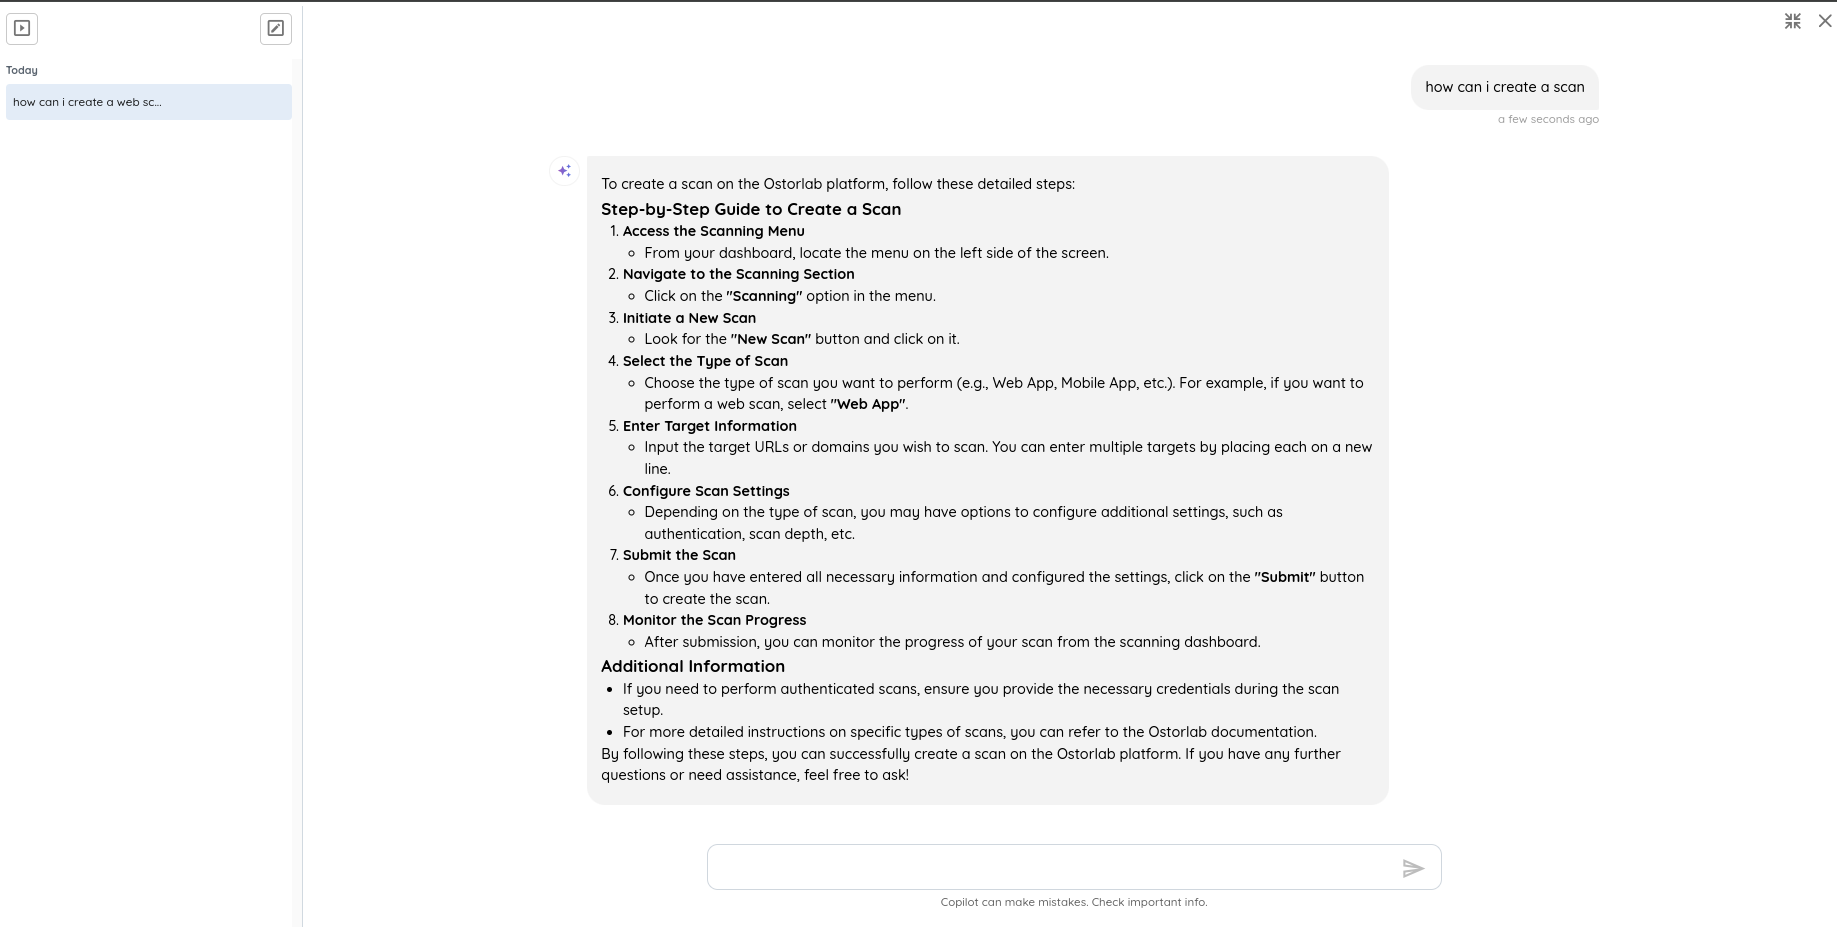
- Enables natural language interaction with platform features
Reporting & Export Enhancements 📈
- Added closed ticket status to scan PDF reports
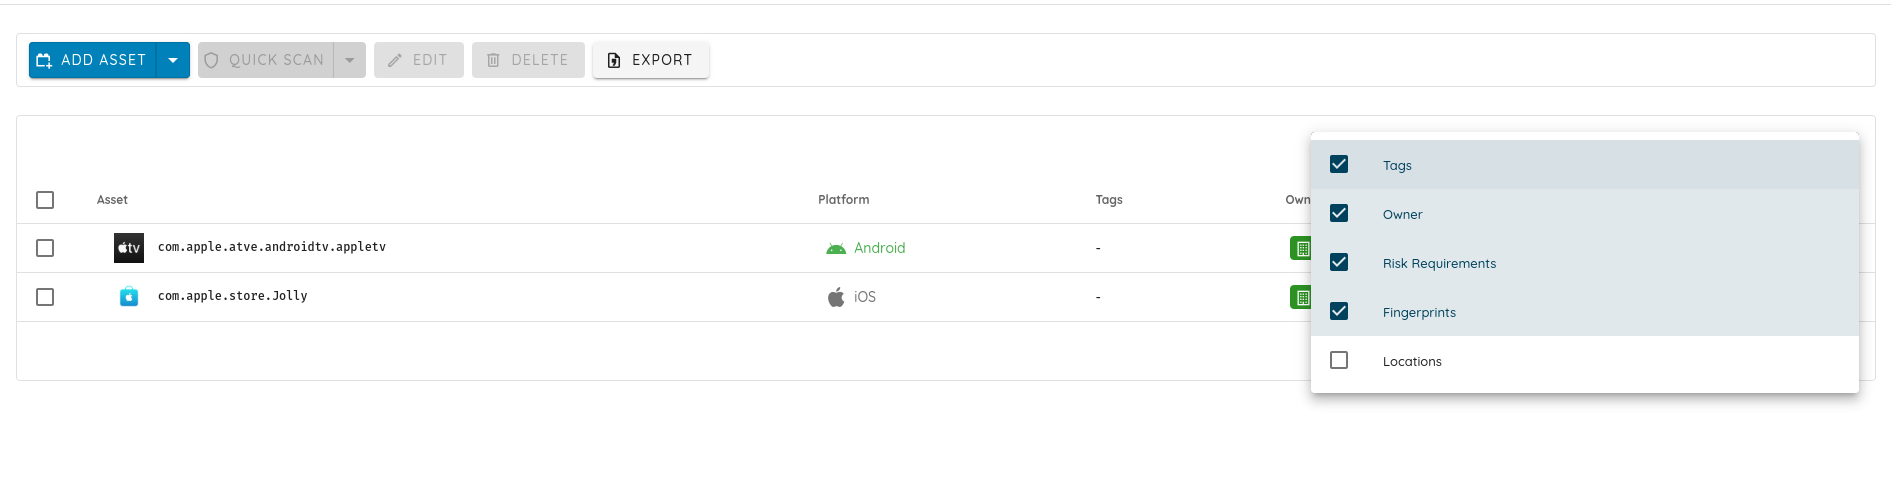
- Implemented filtering for assets CSV exports based on table headers
Detection 🔍
Secret Detection
- Enhanced AWS API key detection
- Enhanced GitHub access token detection
- Added Mapbox secret token detection
Threat Center
Added detection of several fingerprints:
- ThinkPHP
- Wazuh
- SonicWall SSL VPN
- Sophos
- Cyberoam
- Zyxel Devices
- Elber
- .NET Framework
Added support for several CVEs: CVE-2022-47945, CVE-2025-24016, CVE-2025-0108, CVE-2024-53704, CVE-2025-0890, CVE-2025-0674, CVE-2024-29059, CVE-2018-19410, CVE-2024-45195