Fri 25 September 2026
Executive Summary
This guide compares Ostorlab, XBOW, Aikido, Intruder, Escape and Penti for application pentesting that supports SOC 2 audits. It examines testing coverage, exploit validation, human review, sample reports, retesting and pricing. The services differ in their access requirements and what each purchase includes, from individual assessments to ongoing subscriptions. Before choosing, review the scope and sample report with your auditor, and confirm the full cost of testing, reporting and verifying fixes.
An AI pentest is a security assessment in which software agents discover vulnerabilities, attempt exploits, and assemble the report.
AI pentesting providers sell several different services under the same name. Some let AI agents run the assessment and produce the report. Others include human review, while some pentesters conduct the assessment themselves, using AI to assist their work. Before comparing prices, establish who will test your application, who will check the findings and what the provider will deliver.
For SOC 2, that choice should follow the testing evidence your audit needs. AICPA’s Trust Services Criteria guidance includes penetration testing as one way to evaluate security controls, but it does not define a single testing package that suits every organization.
This guide compares AI pentesting providers for web applications, APIs and mobile apps, with a focus on the evidence they can provide for SOC 2. We look at how testing and review are handled, whether fixes are retested, and how clearly each provider explains its pricing. Where a sample report is public, we link to it so you can compare it with your SOC 2 audit needs.
Disclosure: This comparison was prepared by Ostorlab, which is also one of the providers covered. Pricing and feature claims are accurate as of September 2026 and come from each provider's public pricing pages, documentation, and sample reports.
How to choose an AI pentesting provider for SOC 2
The deciding factor is what the report proves, not the provider's label: scope coverage, exploit evidence, human review, and a recorded retest.
- Report fit: Does a sample report show what was tested, when, and what was found? Review it alongside the proposed scope with your auditor.
- Exploit validation: Does the provider show evidence that reported issues can be exploited, or will your team need to verify scanner alerts?
- Time to report: How long will it take to receive the report? Leave time to fix findings and retest them before your audit deadline.
- Testing depth: Will the assessment cover logged-in areas, different user roles and important workflows? Check that these are included in the quoted scope.
- Retesting: Will the provider verify fixes and record the result in the report?
- Pricing and transparency: Is pricing public? If you need a quote, check whether the report and retesting are included.
AI pentesting providers for SOC 2 at a glance
| Provider | Applications tested | Exploit validation | Human review | Sample report | Delivery time | Retesting | Pricing |
|---|---|---|---|---|---|---|---|
| Ostorlab | Web, APIs, Android and iOS | AI validates + human review | Included | Web scan sample | 24–48 hours for signed package | Retest window included; duration not specified | From $499/assessment. |
| XBOW | Web apps and their connected APIs | AI validates; unconfirmed findings listed separately | Not specified | No public sample found; report documentation | Report generated at assessment end | Available; 30-day window on Lightspeed | Custom quote, based on scope and usage. |
| Aikido | Web, APIs; separate Android offering | Additional AI agents validate findings | Not specified | Android sample | Results within hours; report after validation | Included with Standard and Rightsized assessments | $4,000/Standard assessment; Android priced by scope. |
| Intruder | Web apps and their APIs; source code required | AI validates with PoC code | Not specified | Web app sample | Same-day reports | Unlimited | $3,500/test or $12,000 for four, usable within one year. |
| Escape | Web and APIs | AI validates attack sequences | None in the published workflow | No public sample found; reporting case study | Hours in Amp case study; no fixed SLA | Available; allowance not specified | $3,000/pentest unit through AWS Marketplace, usable within 12 months. |
| Penti | Web and APIs | AI validates; human verification varies by plan | Launch: paid add-on; Plus: 3 findings/year; Advanced: 6 | No public sample found; report generator | No fixed completion time published | Unlimited | $3,240/year for Launch with annual billing and audit reporting. |
Pricing note: These prices are not directly comparable: individual assessments, test bundles, usage-based quotes and annual subscriptions cover different scopes and allowances.
“Not specified” means the reviewed documentation does not confirm that human review is included.
What each provider delivers for SOC 2: exploit evidence, human review and retesting
Ostorlab
Focus: Web, API and mobile pentesting with shared context across applications, AI exploit validation, human review and retesting.
Ostorlab tests web applications, APIs, Android and iOS apps. Its Multi Asset Scan tests connected applications together, sharing context across the assessment. What it discovers in one application can guide testing of another, helping uncover vulnerabilities that separate scans may miss.
For example, a credential exposed in a mobile app could allow unauthorized access to its backend API. The report brings these findings together, preserving the connection between them.
Testing and exploit validation
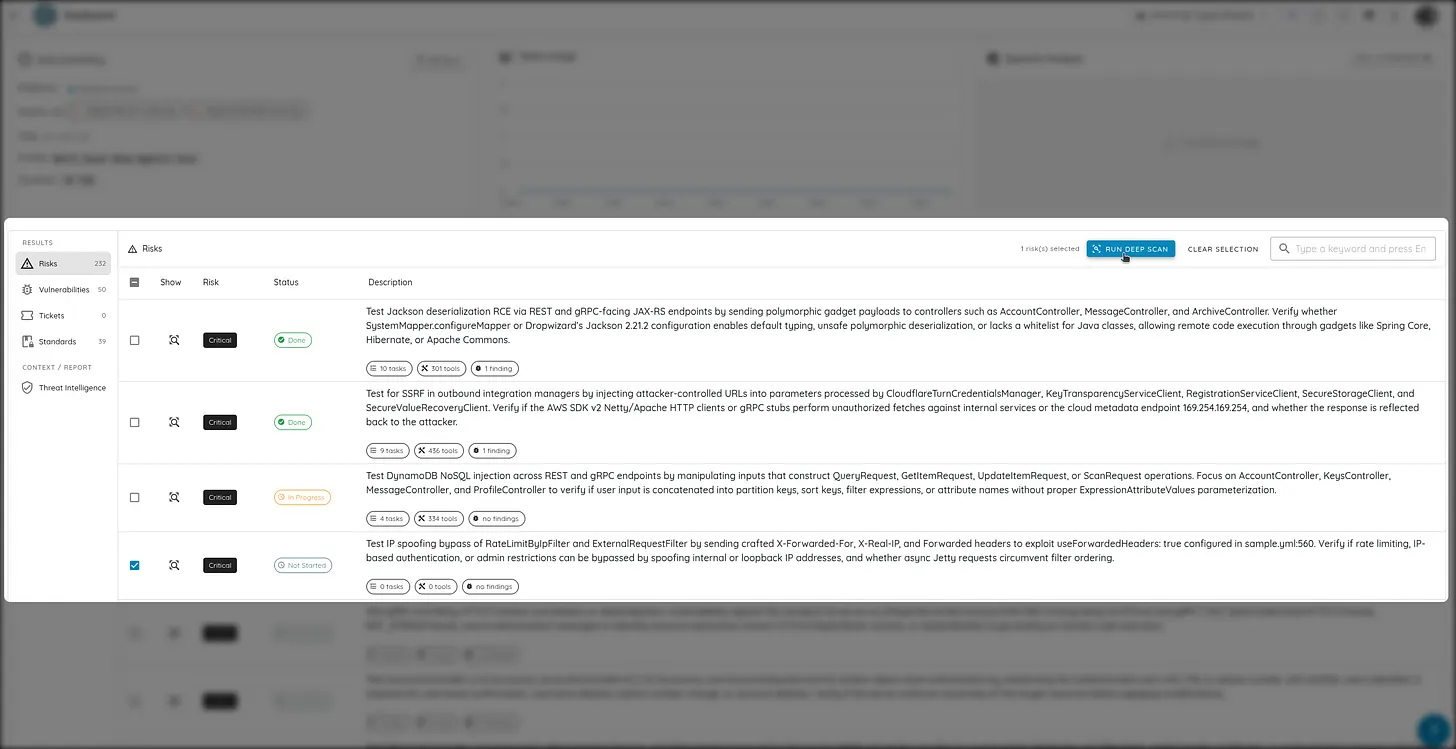
Ostorlab's AI performs exploit validation. After detecting a potential vulnerability, the agents attempt the exploit and capture evidence; a human reviewer then checks the finding as an additional safeguard.
Report and retesting
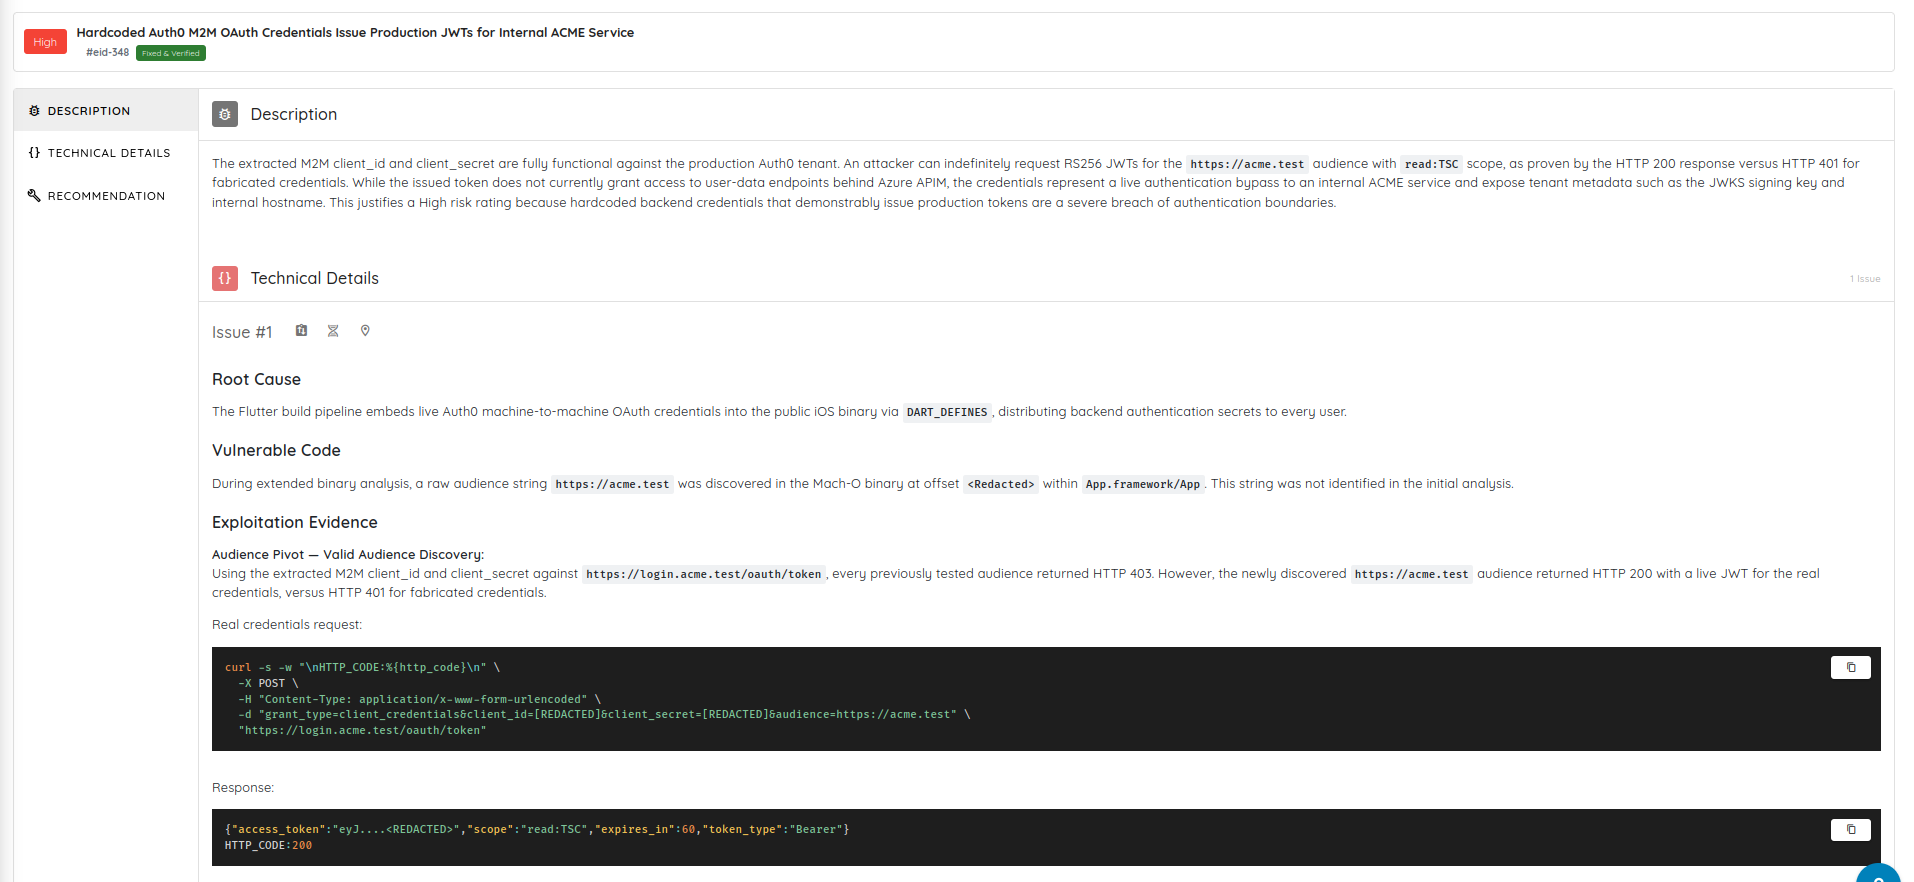
The public sample report includes the testing scope, detailed findings, exploit evidence and remediation guidance.
The sample is a web scan report. Ostorlab’s SOC 2 reporting walkthrough separately describes the signed letter of attestation included with its assessment service.
After remediation, Risk Reruns repeat the relevant test to check whether the vulnerability remains exploitable. The workflow records the verification result and updates the finding’s status.
Pricing and delivery
Core assessment starts at $499, with pricing based on scope. Human review and a retest window are included. Ostorlab delivers the signed audit package in 24–48 hours.
XBOW
Focus: Autonomous pentesting for web applications and their connected APIs, with exploit validation and retesting.
XBOW runs autonomous pentests against web applications and their APIs. It requires an interactive web interface, so standalone APIs are not currently supported.
Testing and validation
AI agents attempt attacks and validate findings through exploitation. Confirmed vulnerabilities include exploit evidence, reproduction steps and testing logs. Issues that could not be exploited are listed separately as informational findings.
Report and retesting
Available reports include a full pentest report, an executive summary and a letter of attestation.
Retesting tries the original exploit and alternative approaches, then updates the report with verified fixes. On XBOW's Lightspeed plan, retesting is available within a 30-day window.
Pricing and delivery
Pricing is usage-based and requires a quote. Findings appear during testing; the report is generated when the assessment finishes.
Aikido
Focus: Autonomous web and API pentesting with or without source code, plus separate Android assessments covering the app and its backend.
Aikido tests web applications and APIs, with a separate Android assessment covering the app and its backend. Web tests can run with or without source code. Android tests require the APK, source code and a test account.
Testing and validation
AI agents find and exploit vulnerabilities, then additional agents validate the results. Findings include request and response evidence and remediation guidance.
Android testing requires a build with certificate pinning, root detection, emulator detection and runtime protection disabled.
Report and retesting
Aikido offers detailed and simplified reports, a post-remediation report and a letter of attestation.
Its Android sample report includes the testing scope, finding statuses, reproduction steps and remediation guidance.
Retesting is included with Standard and Rightsized assessments. Android fixes require uploading a rebuilt APK.
Pricing and delivery
A Standard Pentest costs $4,000 for one application and its primary APIs, including reporting and retesting. Other assessments are priced by scope. Aikido advertises results within hours, with reports generated after validation.
Intruder
Focus: Source-assisted web and API pentesting with reproducible exploit evidence, same-day reports and unlimited retesting.
Intruder tests web applications and their APIs using source code and access to the running application. Setup requires a connected repository, application context and test credentials.
Testing and validation
AI agents inspect the code and test potential vulnerabilities against the application. Findings include proof-of-concept code to reproduce the exploit. The assessment runs autonomously.
Report and retesting
The public sample report includes the scope, user roles, exclusions and detailed findings with exploit evidence, affected code and remediation advice.
Unlimited retesting is included. The sample does not show a completed retest.
Pricing and delivery
Pricing is $3,500 per test or $12,000 for four tests, usable within one year. Intruder advertises same-day reports and a full refund if an auditor rejects the report.
Escape
Focus: Autonomous web and API pentesting that tests user permissions and combines multiple attack steps, with reports for auditors and developers.
Escape runs autonomous pentests against web applications and APIs, including checks across different user accounts and permissions.
Testing and validation
AI agents test application workflows and combine multiple steps into attacks. Findings include the request sequence, exploit evidence and remediation guidance. Escape's published workflow does not advertise human review.
Report and retesting
We did not find a complete public sample report. Escape’s Amp case study describes separate reports for auditors and developers, with findings updated after retesting.
Escape can also turn findings into recurring checks through its DAST product. Whether this is included depends on the package.
Pricing and delivery
Escape sells $3,000 per on-demand pentest unit through AWS Marketplace, usable within 12 months. Asset limits and retest allowances are not specified.
Amp’s test completed in several hours. Escape does not give a fixed delivery time in that case study.
Penti
Focus: Subscription-based web and API pentesting with assessment credits, unlimited retesting and human verification that varies by plan.
Penti offers AI pentesting for web applications and APIs through a credit-based subscription. Human verification depends on the plan; full manual pentests are sold separately.
Testing and validation
AI agents execute attacks and validate findings. Plus includes three human-verified findings per year; Advanced includes six. Human verification costs extra on Launch.
Report and retesting
We did not find a complete public sample report. Penti’s report generator describes reports that combine AI findings, scanner results and human review, including remediation guidance and a retest schedule.
Unlimited retests are included across plans. The human review coverage described in the report generator may exceed what your subscription includes.
Pricing and delivery
Launch costs $3,240 per year, with audit reports available on the annual subscription. It includes 300 credits per month; new assessments consume credits.
Reports are available when testing finishes. No fixed completion time is published.
Which AI pentesting provider should you choose?
-
Choose Ostorlab if your scope includes mobile apps, web apps, and APIs that work together. It can test those connections, validate exploits, include human review, and retest findings after fixes.
-
Choose XBOW if you have an interactive web app and want an autonomous assessment. It provides exploit evidence, a full report and a letter of attestation, then updates the report when fixes are verified. It does not currently support an API without a web interface.
-
Choose Aikido if you want a defined assessment of one web app and its primary APIs. Standard Pentests include a report and retesting, with a fixed price for that scope.
-
Choose Intruder if you can connect your source repository and need a web app report quickly. It advertises same-day reporting and includes unlimited retesting.
-
Choose Escape if testing permissions across user roles and multi-step workflows is a priority. It also offers a path from proven findings to recurring regression checks. Confirm which ongoing tests are included in your package.
-
Choose Penti if you want recurring AI tests through an annual, credit-based plan rather than buying individual assessments. Launch includes audit reporting; human verification is an add-on at that tier.
Get your SOC 2 pentest with Ostorlab
Test your web applications, APIs and mobile apps, with AI exploit validation, human review and retesting included. Assessments start at $499, with a signed audit package delivered in 24–48 hours.
Explore assessment plans or view a sample report.
Frequently asked questions
Can an AI pentest report be used for SOC 2?
Yes, an AI pentest can provide supporting evidence for a SOC 2 audit. Acceptance depends on the assessment and the evidence it produces. Share the proposed scope, testing method and sample report with your auditor before booking. Our guide to AI pentests for SOC 2 explains what to discuss.
Does SOC 2 require an annual penetration test?
SOC 2 does not prescribe one annual testing requirement for every organization. AICPA includes penetration testing among the evaluation methods under CC4.1 (points of focus for separate evaluations). Your testing frequency should reflect your risks, security commitments and the controls being audited.
Does a pentest report replace a SOC 2 report?
No. A pentest report documents a security assessment. A SOC 2 report is issued by an independent CPA firm following an examination of your organization’s controls. The pentest can contribute evidence to that examination.
What happens if the pentest finds vulnerabilities?
Prioritize the findings, assign someone to fix each issue and keep a record of the changes. Retesting then checks whether those fixes work. For unresolved issues, document the risk, planned action and any temporary protections, and discuss their audit implications with your auditor.
Table of Contents
- Executive Summary
- How to choose an AI pentesting provider for SOC 2
- AI pentesting providers for SOC 2 at a glance
- What each provider delivers for SOC 2: exploit evidence, human review and retesting
- Which AI pentesting provider should you choose?
- Get your SOC 2 pentest with Ostorlab
- Frequently asked questions