Spring Security SpEL 注入 RCE,7.1.3 已修复 (CVE-2026-59273)
Spring Security 的 ELRequestMatcher 在允许类型引用的 SpEL 上下文中求值,当外部输入绑定到 RequestMatcher 属性时可导致 RCE;7.1.3 和 7.0.9 已修复。
TL;DR
- Spring Security 的
ELRequestMatcher在允许类型引用和静态方法调用的上下文中求值 SpEL 表达式。当应用程序把外部输入绑定到RequestMatcher属性时,绑定的字符串就会成为该表达式。 - Spring Security 7.1.0 至 7.1.2、7.0.0 至 7.0.8,以及 6.5、6.4、5.8、5.7 分支受影响。仅使用该库无法被远程触达;应用程序必须把外部输入绑定到
RequestMatcher。 - Spring 将该漏洞评为严重,CVSS v3.1 9.8。2026-11-20 和 2026-11-21 出现的两个公开概念验证仓库展示了类型引用,但没有展示命令执行。截至 2026-11-22,未发现野外利用,该 CVE 也未列入 CISA KEV。
- 升级到 Spring Security 7.1.3、7.0.9 或 7.2.0,或升级到 Spring Boot 4.1.3、4.0.10 或 4.2.0。6.5、6.4、5.8 和 5.7 的修复仅限 Enterprise 支持。如果无法升级,请删除所有从外部输入到
RequestMatcher属性的绑定。
我受影响吗?
应用程序必须同时满足以下所有条件才会暴露:
- 使用受影响的 Spring Security 版本:7.1.0 至 7.1.2、7.0.0 至 7.0.8、6.5.0 至 6.5.12、6.4.0 至 6.4.19、5.8.0 至 5.8.28,或 5.7.26 及更早版本。
- 控制器、表单对象或其他 Bean 把请求值绑定到
RequestMatcher类型的属性,因此 Spring 的数据绑定器会用攻击者控制的文本创建ELRequestMatcher。 - 该 matcher 在攻击者可触达的请求上求值。
- 绑定的字符串没有被限制为文档中的
hasIpAddress和hasHeader操作。
该类也会直接用于配置,例如 DelegatingAuthenticationEntryPoint 的映射。用代码中的固定字符串构建的 matcher 不受攻击者控制。暴露来自数据绑定,而不是类本身。
| 分支 | 受影响版本 | 修复版本 |
|---|---|---|
| 7.2.x | 无 | 7.2.0 (OSS) |
| 7.1.x | 7.1.0 至 7.1.2 | 7.1.3 (OSS) |
| 7.0.x | 7.0.0 至 7.0.8 | 7.0.9 (OSS) |
| 6.5.x | 6.5.0 至 6.5.12 | 6.5.13(仅限 Enterprise 支持) |
| 6.4.x | 6.4.0 至 6.4.19 | 6.4.20(仅限 Enterprise 支持) |
| 5.8.x | 5.8.0 至 5.8.28 | 5.8.29(仅限 Enterprise 支持) |
| 5.7.x 及更早 | 5.7.26 及更早 | 5.7.27(仅限 Enterprise 支持) |
Spring 将该漏洞评为严重,CVSS v3.1 9.8(CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H)。Spring 于 2026-11-19 在 Maven Central 发布了 7.1.3、7.0.9 和 7.2.0。2026-11-22 检查时,6.5.13、6.4.20、5.8.29 和 5.7.27 工件不在 Maven Central 上,Spring 将这些版本列为仅限 Enterprise 支持。
检查应用程序解析到的版本:
mvn dependency:tree -Dincludes=org.springframework.security:spring-security-web,org.springframework.security:spring-security-core
./gradlew dependencyInsight --dependency spring-security-web --configuration runtimeClasspath
对于已打包的应用程序,检查 jar:
unzip -l app.jar | grep 'spring-security-web'
对于 Spring Boot 应用程序,打印受管理的 Spring Security 版本:
./mvnw help:evaluate -Dexpression=spring-security.version -q -DforceStdout
然后在源代码中查找绑定点:
grep -rn "RequestMatcher" src/main/java
grep -rn "ELRequestMatcher" src/main/java
依赖检查会打印版本。源代码搜索会找到 RequestMatcher 字段。检查绑定该字段的控制器或表单对象,确认请求数据能否设置它。在 @Bean 方法中用固定字符串配置的 matcher 不是易受攻击的路径。
如何修复?
升级到已修复的 Spring Security 版本。Spring Boot 4.1.3、4.0.10 和 4.2.0 分别管理 Spring Security 7.1.3、7.0.9 和 7.2.0,因此对 Boot 应用程序来说,升级父级或插件是最短路径。
- 在 Maven 中修改 Spring Boot 父级:
<parent>
  <groupId>org.springframework.boot</groupId>
  <artifactId>spring-boot-starter-parent</artifactId>
  <version>4.1.3</version>
</parent>
- 或在 Gradle 中修改 Spring Boot 插件:
plugins {
  id 'org.springframework.boot' version '4.1.3'
}
- 对于直接声明 Spring Security 的应用程序,提高依赖版本:
<dependency>
  <groupId>org.springframework.security</groupId>
  <artifactId>spring-security-web</artifactId>
  <version>7.1.3</version>
</dependency>
implementation 'org.springframework.security:spring-security-web:7.1.3'
- 重新构建、重新部署并重启应用程序。运行中的进程会保留旧类,直到重启。
6.5、6.4、5.8 或 5.7 分支的应用程序需要该分支的商业补丁。公共 Maven Central 不提供 6.5.13、6.4.20、5.8.29 或 5.7.27。最新的 3.5 版本 Spring Boot 3.5.16 管理 Spring Security 6.5.11,因此 Boot 3.5 应用程序如果没有升级到 4.x 或签订支持合同,就没有公开的修复工件。
如果现在无法升级,请删除绑定点:
- 找到 Spring 从请求数据绑定的每个
RequestMatcher类型属性。 - 从可绑定对象中删除该属性,或将其设为只读并在代码中设置。
- 如果该值必须可配置,只接受固定名称,并用常量构建 matcher。
- 不要把过滤 SpEL 字符串当作长期修复。解析器接受许多等价形式,受支持的修复是受限的求值上下文。
公告没有列出既能让 matcher 继续使用又安全的配置开关。限制绑定是应用程序层面的变通方法,不是供应商支持的设置。
根本原因是什么?
ELRequestMatcher 保存 SpEL 表达式,并在 StandardEvaluationContext 中求值,该上下文允许类型引用、构造器、静态方法调用、Bean 引用和任意属性访问。matcher 只需要根对象上的 hasIpAddress() 和 hasHeader(),但上下文没有把求值限制在这两个方法上。
易受攻击的代码位于标签 7.1.2 的 web/src/main/java/org/springframework/security/web/util/matcher/ELRequestMatcher.java。第 47 至 50 行的构造器解析字符串:
public ELRequestMatcher(String el) {
    SpelExpressionParser parser = new SpelExpressionParser();
    this.expression = parser.parseExpression(el);
}
第 53 至 60 行的 matches() 创建上下文,第 66 至 68 行的 createELContext() 返回该上下文:
@Override
public boolean matches(HttpServletRequest request) {
    EvaluationContext context = createELContext(request);
    Boolean result = this.expression.getValue(context, Boolean.class);
    Assert.notNull(result,
            "The expression " + this.expression.getExpressionString() + " returned null. Expected true|false");
    return result;
}

public EvaluationContext createELContext(HttpServletRequest request) {
    return new StandardEvaluationContext(new ELRequestMatcherContext(request));
}
根对象公开两个文档中的方法:
class ELRequestMatcherContext {

    private final HttpServletRequest request;

    ELRequestMatcherContext(HttpServletRequest request) {
        this.request = request;
    }

    public boolean hasIpAddress(String ipAddress) {
        return (new IpAddressMatcher(ipAddress).matches(this.request));
    }

    public boolean hasHeader(String headerName, String value) {
        String header = this.request.getHeader(headerName);
        return StringUtils.hasText(header) && header.contains(value);
    }
}
StandardEvaluationContext 不会把表达式限制在根对象上。像 T(java.lang.Math).abs(-1) == 1 这样的表达式会直接解析 java.lang.Math 类型,即使 ELRequestMatcherContext 没有 abs 方法。
另一半是数据绑定。Spring Security 为该类型提供了属性编辑器:
public class RequestMatcherEditor extends PropertyEditorSupport {

    @Override
    public void setAsText(String text) throws IllegalArgumentException {
        setValue(new ELRequestMatcher(text));
    }
}
Spring 的数据绑定器按命名约定发现编辑器,因此 RequestMatcher 属性接受字符串并将其转换为 ELRequestMatcher。公开测试工具发现,在标准类路径上,即使没有注册编辑器,绑定也能通过 ELRequestMatcher(String) 构造器成功。两条路径都会把攻击者控制的文本变成表达式。
如何被利用?
攻击者把 SpEL 表达式作为应用程序绑定到 RequestMatcher 属性的值发送。matcher 运行时,表达式以应用程序的权限求值。
- 应用程序公开一个请求参数、表单字段或 JSON 属性,它映射到
RequestMatcher属性。 - 攻击者在该字段中提供 SpEL 表达式。
- Spring 把字符串转换为
ELRequestMatcher并保存到对象上。 - 后续请求到达 matcher,
matches()对表达式求值。 T(...)类型引用解析一个类,静态方法或构造器执行。- 表达式在应用程序进程中执行代码。
公开测试工具展示了这条链的前半部分,但没有执行命令:
ELRequestMatcher requestMatcher = new ELRequestMatcher("T(java.lang.Math).abs(-1) == 1");
requestMatcher.matches(new MockHttpServletRequest());
在 7.1.2 上,表达式匹配。在 7.1.3 上,同一表达式抛出 SpelEvaluationException。测试工具使用 Math.abs,其 README 说明不包含进程载荷。公告把影响描述为远程代码执行。公开材料证明的是类型引用,不是武器化的命令链。
攻击如何展开?
攻击者控制的文本通过数据绑定成为 ELRequestMatcher,matcher 在允许类型访问的上下文中求值,因此 SpEL 类型引用可以以应用程序权限执行代码。
RequestMatcher 属性"] --> B["Spring 数据绑定器
把字符串转换为 ELRequestMatcher"] B --> C["构造器解析
SpEL 表达式"] C --> D["matches 构建上下文
不限制类型引用"] D --> E["T(...) 解析类
并执行静态方法"] E --> F["代码在应用程序
进程中执行"]
攻击者能做什么?
控制绑定值的攻击者可以在应用程序进程中执行代码。公告将该影响评为远程代码执行。公开测试工具证明了类型引用步骤,并在命令之前停止。
- 以应用程序用户身份执行命令。 应用程序的文件权限、环境变量和网络访问成为攻击者的起点。
- 读取应用程序机密。 进程能读取的配置属性、数据库凭据和云凭据都可被访问。
- 修改应用程序数据。 表达式在请求线程中运行,可以使用应用程序的类路径和进程状态。
- 到达其他系统。 应用程序的网络位置和信任关系决定攻击者能走多远。
这里列出所有条件。应用程序必须使用受影响版本。它必须把外部输入绑定到 RequestMatcher 属性。攻击者必须控制绑定的字符串。matcher 必须在攻击者可触达的请求上求值。绑定端点公开时不需要认证。仅用代码中的固定字符串构建 matcher 的应用程序,即使使用受影响版本也不会暴露。
为什么修复有效?
修复把 StandardEvaluationContext 替换为 SimpleEvaluationContext,该上下文禁用类型引用、构造器、Bean 引用和任意方法调用。withInstanceMethods() 选项保留 matcher 文档中的两个实例方法。
-import org.springframework.expression.spel.support.StandardEvaluationContext;
+import org.springframework.expression.spel.support.SimpleEvaluationContext;
@@
-   public EvaluationContext createELContext(HttpServletRequest request) {
-       return new StandardEvaluationContext(new ELRequestMatcherContext(request));
-   }
+   public EvaluationContext createELContext(HttpServletRequest request) {
+       return SimpleEvaluationContext.forReadOnlyDataBinding()
+           .withInstanceMethods()
+           .withRootObject(new ELRequestMatcherContext(request))
+           .build();
+   }
SimpleEvaluationContext.forReadOnlyDataBinding() 允许读取属性,但不允许写入。withInstanceMethods() 允许调用根对象上的方法,这正是 hasIpAddress('10.0.0.0/8') 和 hasHeader('User-Agent', 'curl') 需要的。上下文不再解析 T(java.lang.System),也不再对 hasIpAddress() 的结果调用 getClass()。修复提交为这两种情况添加了回归测试。
该修复对 ELRequestMatcher 路径是完整的。如果子类覆盖 createELContext 并返回自己的 StandardEvaluationContext,旧行为会保留,因此升级时要检查这类覆盖。
如何检查是否已遭入侵?
该 CVE 没有公开的入侵指标。表达式在内存中运行,可能不会在应用程序日志中留下记录,因此没有告警并不证明没有尝试。
先检查请求日志。正常部署中的 matcher 表达式调用 hasIpAddress 或 hasHeader。请求参数中出现 T( 或其编码形式 %54%28 值得调查:
grep -Ei 'T\(|%54%28' /var/log/nginx/access.log /var/log/apache2/access.log 2>/dev/null
在异常请求前后检查应用程序日志中的 SpelEvaluationException。失败的表达式可能在执行前抛出异常:
grep -i "SpelEvaluationException" /var/log/spring-app.log
检查 Java 进程启动的子进程,以及不符合应用程序正常出站流量的连接:
ps -eo pid,ppid,user,args | grep -E '[j]ava|[b]ash|[c]url|[w]get'
请求日志中的 T( 是线索,不是利用证据。失败的表达式可能不留痕迹。如果应用程序覆盖了 createELContext,请单独审查该代码。
时间线
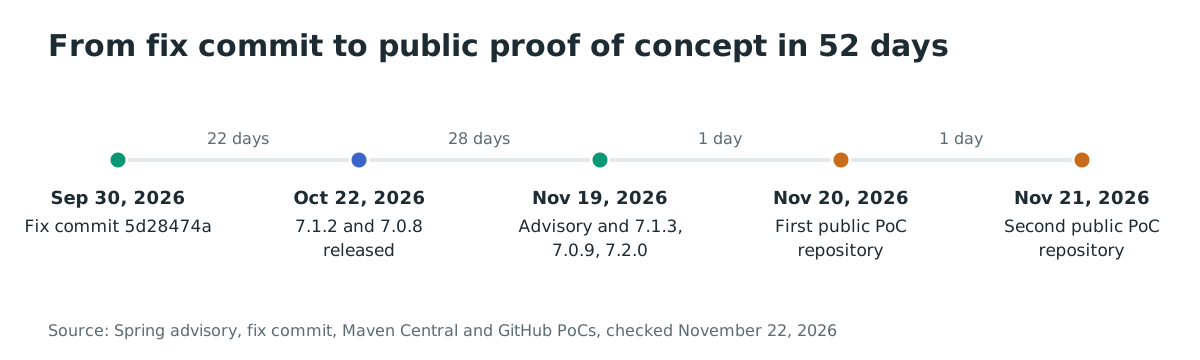
- 2026-09-30:修复提交
5d28474a5cef在 Spring Security 仓库中创建。 - 2026-10-22:最后一个易受攻击的开源工件 Spring Security 7.1.2 和 7.0.8 发布。
- 2026-11-19:Spring 发布公告,并在 Maven Central 发布 7.1.3、7.0.9 和 7.2.0。
- 2026-11-20:第一个公开概念验证仓库出现。
- 2026-11-21:第二个公开概念验证仓库于 21:26 UTC 出现。
常见问题
所有 Spring Security 应用程序都需要修复吗?
不需要。仅使用该库无法被远程触达。只有当应用程序把外部输入绑定到 RequestMatcher 属性并求值该 matcher 时才会暴露。仅用代码中的固定字符串构建 matcher 的应用程序仍应升级,但暴露程度不同。
有公开利用代码吗?
有两个公开概念验证仓库。较实质的一个是差分测试工具,它显示 T(java.lang.Math) 在 7.1.2 上解析,在 7.1.3 上抛出异常。它不包含进程载荷,也没有展示命令执行。
CVE-2026-59273 已在野外被利用吗?
截至 2026-11-22,未发现野外利用,该 CVE 未列入 CISA KEV。公开材料是实验室测试工具,不是攻击报告。
哪个 Spring Boot 版本修复了该漏洞?
Spring Boot 4.1.3 管理 Spring Security 7.1.3,Spring Boot 4.0.10 管理 7.0.9,Spring Boot 4.2.0 管理 7.2.0。Spring Boot 3.5.16 仍管理 6.5.11,而 6.5.13 修复仅限 Enterprise 支持。
我还能继续使用 ELRequestMatcher 吗?
可以,在修复版本上,当表达式来自可信代码时。修复保留了 hasIpAddress 和 hasHeader。不要从请求数据中接受表达式。
DelegatingAuthenticationEntryPoint 会让我易受攻击吗?
它本身不会。它的 matcher 映射通常由配置中的固定字符串构建。易受攻击的路径是 Spring 数据绑定器从请求输入填充的 RequestMatcher 属性。
参考文献
- CVE-2026-59273 的 Spring Security 安全公告,2026-11-19 发布(2026 年 11 月 22 日检查):https://spring.io/security/cve-2026-59273
- 修复提交 5d28474a5cef,标题 "Fix ELRequestMatcher to use restricted SpEL evaluation context",2026-09-30 创建(2026 年 11 月 22 日检查):https://github.com/spring-projects/spring-security/commit/5d28474a5cefab43d41b0da8c487ce40df957855
- 标签 7.1.2 的易受攻击
ELRequestMatcher(2026 年 11 月 22 日检查):https://github.com/spring-projects/spring-security/blob/7.1.2/web/src/main/java/org/springframework/security/web/util/matcher/ELRequestMatcher.java - 标签 7.1.3 的修复版
ELRequestMatcher(2026 年 11 月 22 日检查):https://github.com/spring-projects/spring-security/blob/7.1.3/web/src/main/java/org/springframework/security/web/util/matcher/ELRequestMatcher.java - 标签 7.1.2 的
RequestMatcherEditor(2026 年 11 月 22 日检查):https://github.com/spring-projects/spring-security/blob/7.1.2/web/src/main/java/org/springframework/security/web/util/matcher/RequestMatcherEditor.java - Spring Security 7.1.3 版本,2026-11-20 发布(2026 年 11 月 22 日检查):https://github.com/spring-projects/spring-security/releases/tag/7.1.3
- Spring Security 7.0.9 版本,2026-11-20 发布(2026 年 11 月 22 日检查):https://github.com/spring-projects/spring-security/releases/tag/7.0.9
- Spring Security 7.2.0 版本,2026-11-20 发布(2026 年 11 月 22 日检查):https://github.com/spring-projects/spring-security/releases/tag/7.2.0
- Spring Boot 4.1.3 版本,2026-11-19 发布(2026 年 11 月 22 日检查):https://github.com/spring-projects/spring-boot/releases/tag/v4.1.3
- Spring Boot 4.0.10 版本,2026-11-19 发布(2026 年 11 月 22 日检查):https://github.com/spring-projects/spring-boot/releases/tag/v4.0.10
- Spring Boot 4.2.0 版本,2026-11-19 发布(2026 年 11 月 22 日检查):https://github.com/spring-projects/spring-boot/releases/tag/v4.2.0
- Spring Boot 3.5.16 版本,2026-06-25 发布(2026 年 11 月 22 日检查):https://github.com/spring-projects/spring-boot/releases/tag/v3.5.16
- Spring Boot 3.5.16 依赖管理,固定 Spring Security 6.5.11(2026 年 11 月 22 日检查):https://repo1.maven.org/maven2/org/springframework/boot/spring-boot-dependencies/3.5.16/spring-boot-dependencies-3.5.16.pom
- Maven Central 上的 Spring Security 7.1.3 工件(2026 年 11 月 22 日检查):https://repo1.maven.org/maven2/org/springframework/security/spring-security-core/7.1.3/
- Abraxas Labs 的公开测试工具,2026-11-21 创建(2026 年 11 月 22 日检查):https://github.com/abraxas/cve-2026-59273-spring-security-elmatcher
- afernandesvigo 的公开概念验证仓库,2026-11-20 创建(2026 年 11 月 22 日检查):https://github.com/afernandesvigo/PoC-CVE-2026-59273
- CWE-94,Improper Control of Generation of Code(2026 年 11 月 22 日检查):https://cwe.mitre.org/data/definitions/94.html
- CWE-95,Improper Neutralization of Directives in Dynamically Evaluated Code(2026 年 11 月 22 日检查):https://cwe.mitre.org/data/definitions/95.html
- CWE-470,Use of Externally-Controlled Input to Select Classes or Code(2026 年 11 月 22 日检查):https://cwe.mitre.org/data/definitions/470.html
- CISA Known Exploited Vulnerabilities 目录,2026-11-22 检查 CVE-2026-59273:https://www.cisa.gov/known-exploited-vulnerabilities-catalog